Recovery Point Objective: Why Data Gaps Drive Ransomware Success
Recovery point objective defines the maximum acceptable data loss window, forcing teams to accept financial trade-offs between storage costs and business continuity risks.
Recovery point objective defines the maximum acceptable data loss window, forcing teams to accept financial trade-offs between storage costs and business continuity risks.
These tools transform raw data into actionable context by correlating indicators across multiple sources, revealing hidden attack patterns that isolated alerts miss.

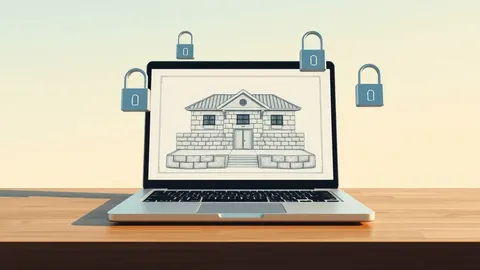
Your laptop operates like a fortified house where the operating system acts as the foundation, and every application is a window that requires specific locking mechanisms to remain secure.

Watermarking fails against extraction attacks, while input validation and output limiting provide measurable barriers to unauthorized model replication.

Secure Access Service Edge includes network functions while Secure Service Edge focuses only on application security, creating distinct operational costs.

A computer virus is a specific replication method, while malware is the broad category of all hostile software that includes viruses, worms, and trojans.

Unmanaged user access creates hidden data exposure that grows faster than revenue, requiring automated identity controls rather than manual oversight.

Firmware malware resides below the operating system, allowing it to survive disk wipes, OS reinstalls, and even hardware swaps by persisting in the device's read-only memory layers.

Most recovery efforts fail because users prioritize deleting content over severing the technical links that allow the attacker to maintain access to your accounts.

Memory corruption manifests as silent state drift and control flow hijacking, often hiding in valid-looking logs until a crash occurs.

Quantum computers exploit superposition to solve mathematical problems that secure modern internet traffic, rendering current encryption methods obsolete.

Attackers rarely break into SaaS software directly; they steal the digital keys you already hold to walk through the front door with full authority.

WPA3 stops offline password attacks but forces older devices off secure networks, creating a management trade-off you must accept.

Static credentials on long-lived service accounts create persistent backdoors that bypass human-led identity controls and survive employee turnover.

Security culture is the invisible layer of shared assumptions that determines whether technical controls succeed or fail during an incident response.

Background location tracking often hides in seemingly harmless app behaviors, draining battery and mapping your movements without explicit consent.

Moving computation closer to data sources reduces latency and bandwidth costs while creating new attack surfaces that central models ignore

Attackers exploit human psychology faster than technical controls can intercept, making behavioral anomalies the primary detection vector for compromise attempts.

Execute precise containment and recovery steps when third-party cookie deprecation exposes tracking gaps or data leakage in your web properties.

Trace the exact path from package upload to execution, identifying the specific trust gaps attackers exploit and where you can break the chain.