Researcher Details Hardware Tampering and UART Lockdowns in WiFi Security Study
A security researcher shares findings on physical tampering, damaged flash chips, and UART restrictions uncovered during a hardware analysis.
Key points
- Researcher /u/gid0rah submitted a report detailing WiFi secrets and hardware lockdowns.
- The study involved physical tampering that resulted in a damaged flash memory chip.
- UART lockdowns were identified as part of the device's security mechanisms.
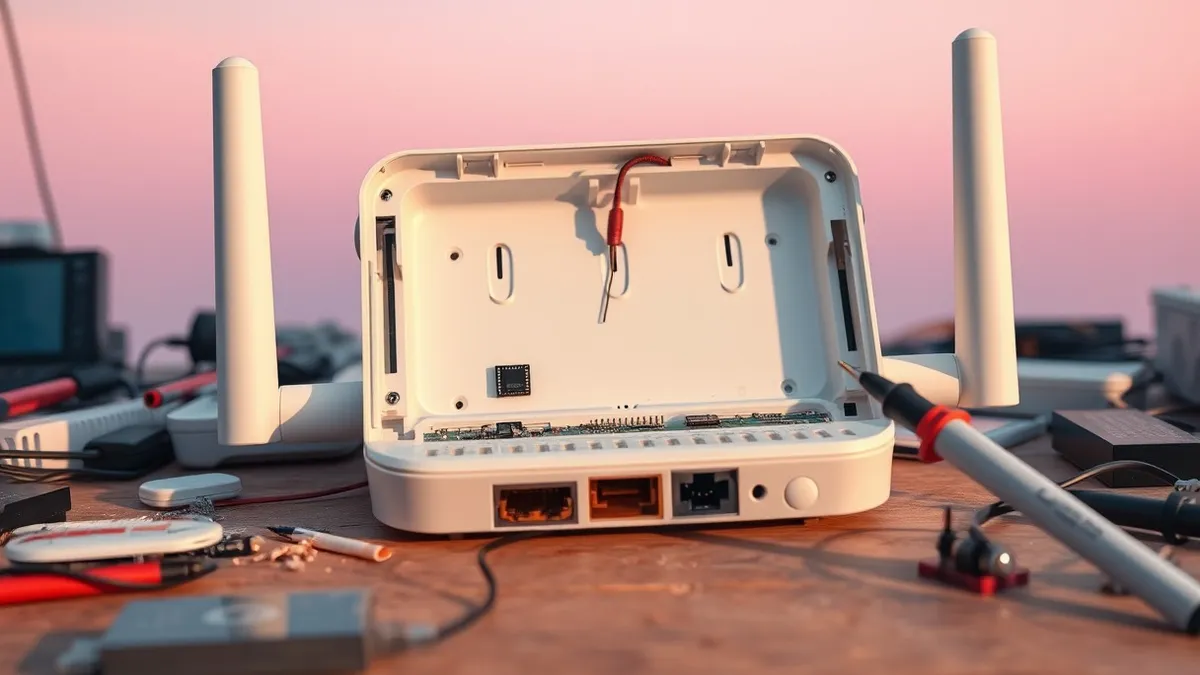
A security researcher known as /u/gid0rah submitted a detailed report to the r/netsec subreddit outlining findings from a hardware security analysis. The submission, titled "A story of wifi secrets, UART lockdowns and a damaged flash memory chip," reveals the challenges and physical consequences encountered during the investigation of network device security mechanisms.
The report highlights specific technical hurdles faced during the analysis, including the implementation of UART lockdowns that restrict access to device interfaces. The researcher noted that the process of bypassing these security measures involved physical manipulation of the hardware, which ultimately led to the damage of a flash memory chip. This physical degradation underscores the risks associated with invasive hardware tampering techniques.
Context and Background
The submission to r/netsec serves as a primary source for these findings, providing a narrative of the technical obstacles encountered. According to the post summary provided on the platform, the core of the story revolves around the extraction of WiFi secrets and the methods used to overcome interface restrictions. The mention of UART lockdowns indicates that the device manufacturer implemented specific safeguards to prevent unauthorized access via universal asynchronous receiver-transmitter ports.
These lockdowns are designed to prevent attackers from gaining command-line access or reading sensitive data directly from the hardware interface. The researcher’s experience suggests that bypassing such measures is not straightforward and may require destructive physical interventions. The damage to the flash memory chip mentioned in the title implies that the attempt to access or modify stored data resulted in permanent hardware failure, a common risk in hardware security research.
Who Is Affected
The findings are primarily relevant to security professionals, hardware researchers, and individuals interested in the physical security of network devices. The report does not specify a particular vendor or product model, but the techniques described—UART lockdowns and flash memory protection—are common in consumer and enterprise WiFi routers. Users who rely on the physical integrity of their network hardware should be aware that invasive security testing can lead to device destruction.
Security teams monitoring for hardware-based vulnerabilities may find value in understanding the limitations and risks of physical access attacks. The report serves as a case study in the trade-offs between security hardening and hardware durability. While the specific device is not named, the principles apply to any embedded system that utilizes UART interfaces for debugging or maintenance.
What should you do?
Security professionals should review the physical security controls of their network infrastructure, ensuring that hardware access is restricted to authorized personnel only. Organizations should assess the risk of physical tampering with routers and other network devices, particularly in environments where unauthorized access is possible. Monitoring for unusual hardware behavior or signs of physical manipulation can help detect potential security breaches.
What to do and how to stay safe: WiFi security
- Restrict physical access to network devices such as routers and switches to authorized personnel only.
- Monitor hardware devices for signs of physical tampering, such as broken seals or damaged ports.
- Implement network segmentation to limit the impact of any potential compromise of a single device.
- Review firmware update policies to ensure devices are running the latest security patches when available.
General security guidance from the Threat Times newsroom. It is not confirmed advice from the organisations named in this story.
Frequently asked questions
What specific vulnerability was discovered in the report?
The report describes a scenario involving WiFi secrets and UART lockdowns, but does not detail a specific software vulnerability or CVE.
Did the researcher successfully extract the WiFi secrets?
The source material does not confirm whether the secrets were successfully extracted, only that the attempt damaged a flash memory chip.
Which vendor or product is affected by these findings?
The submission does not name a specific vendor, product, or model; it refers generally to hardware security mechanisms.