Modder cracks Xbox 360 with $4 microcontroller after nine-year effort
A Scottish hacker successfully glitch-hacked a console using a Raspberry Pi Pico, marking the end of a long-term project to bypass security.
Key points
- The exploit uses voltage glitching on the CPU reset pin to bypass cryptography.
- A Raspberry Pi Pico replaces expensive, complex legacy modding hardware.
- The achievement concludes a nine-year research effort by the researcher.
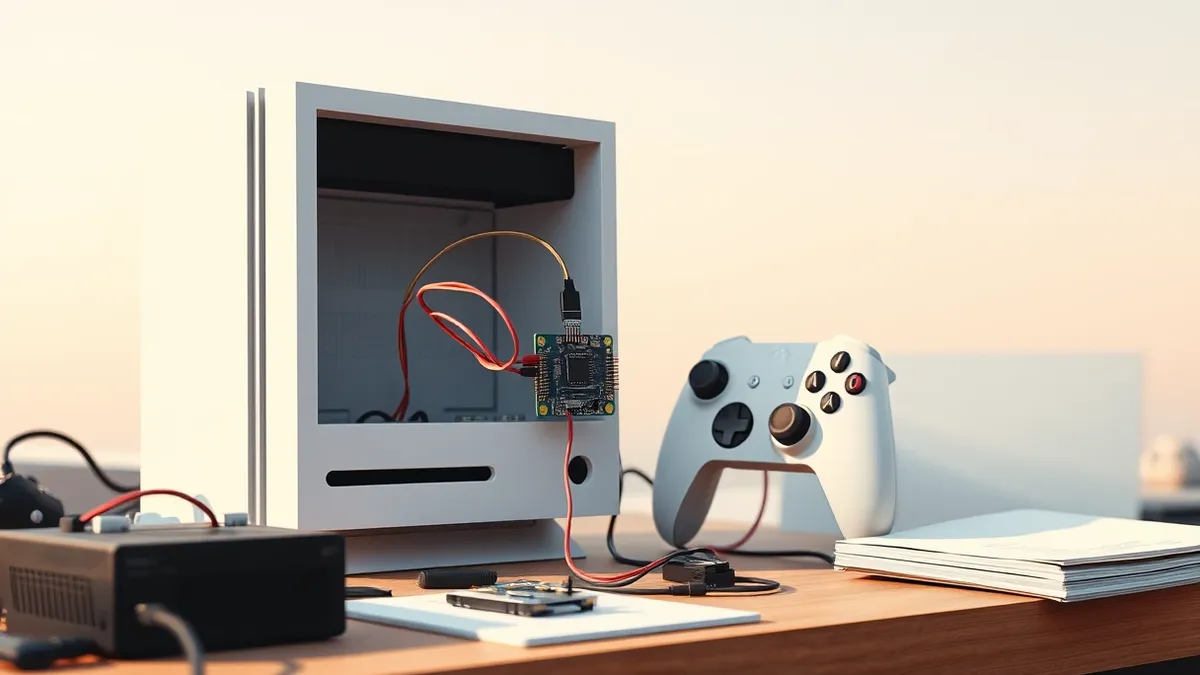
A Scottish hacker named Joshua Kennedy successfully compromised an Xbox 360 console using a low-cost Raspberry Pi Pico microcontroller. According to Tom's Hardware, this operation marks the culmination of a nine-year effort to perfect a voltage-glitching exploit that bypasses the console's security layers.
Kennedy utilized the $4 microcontroller to send precise electrical signals directly into the CPU's reset pin. This action causes the processor to execute instructions incorrectly, allowing unauthorized code execution. The method effectively circumvents Microsoft's cryptographic protections without relying on previously patched software vulnerabilities.
Technical Context and History
The Xbox 360 has faced multiple hardware and firmware exploits since its release. Early methods included modded DVD firmware in 2006 and a hypervisor hack in 2007. In 2009, a wiring hack exposed JTAG debugging ports. The most durable physical intrusion method was the 2011 CPU force-reset exploit, which required specialized hardware and a dedicated voltage-glitching chip to function reliably.
Kennedy previously attempted this exploit in 2017 using a Matrix Coolrunner Rev D modchip board. That approach required extensive soldering of wires, NAND components, and programmers. He also tried building custom programmers using an old PC's parallel port but abandoned the project due to complexity and lack of success, shelving the idea for years.
Hardware Evolution and Execution
The breakthrough in 2026 came with the availability of the Raspberry Pi Pico. This highly capable microcontroller offered the necessary precision and programmability at a fraction of the cost of previous tools. Kennedy connected the Pico to the console's NAND interface header to dump the firmware using the PicoFlasher utility. This step was crucial for accessing the system's stored data.
The process likely involved patching the dumped NAND data with XeLL and reuploading it to the console. While the specific post does not confirm this step, it is a standard procedure for this type of modification. The success of this method highlights how affordable modern microcontrollers can replicate complex, previously expensive hardware hacking techniques.
What should you do?
Console owners should be aware that physical access to their devices can lead to complete system compromise. While this specific exploit requires opening the hardware, it demonstrates the persistence of hardware-level vulnerabilities. Users concerned about warranty or security should keep their consoles in secure locations.
What to do and how to stay safe: Xbox 360
- Keep gaming consoles in physically secure locations to prevent unauthorized hardware access.
- Regularly check for official firmware updates to patch known software vulnerabilities.
- Monitor reputable security news sources for announcements regarding new hardware exploits.
- Consider using network segmentation to isolate gaming devices from sensitive data networks.
Step-by-step guide: Mobile Device Security: How to Protect Data Beyond Passwords
General security guidance from the Threat Times newsroom. It is not confirmed advice from the organisations named in this story.
Frequently asked questions
Does this exploit require software updates from Microsoft?
No, the exploit is a hardware-based voltage glitch that bypasses software cryptography layers entirely.
How much did the primary tool for this hack cost?
The Raspberry Pi Pico microcontroller used in the exploit costs approximately $4.
Is there a patch for this specific hardware vulnerability?
The source material does not mention a software patch for this hardware-level CPU glitching method.