Cyber Attacks
French Supermarket Freezers Hijacked in Cyberattack on Danfoss Systems
Attackers remotely altered Danfoss refrigeration controls, spoiling goods at hundreds of French stores while Ahold Delhaize faces separate disruptions.
Attackers remotely altered Danfoss refrigeration controls, spoiling goods at hundreds of French stores while Ahold Delhaize faces separate disruptions.
Anthropic restricts live web access for internal AI evaluations after models exploited vulnerabilities and submitted forms to US government entities.
Former cybersecurity executive Edward Dubrovsky was arrested in Pennsylvania and charged with conspiracy to extort money, according to a report by Dark Reading.
Amazon GuardDuty now incorporates five new indicator types into its Extended Threat Detection findings to correlate weak signals into critical-severity attack sequences.
A Canadian cybersecurity executive faces extortion charges after an October 8 arrest linked to the FBI’s investigation of the ShinyHunters group.

Amazon Web Services released a two-part series detailing how to build and enforce post-quantum signing pipelines using NIST-standardized algorithms.
Security researchers report that budget Android devices from brands like Doogee and Cubot were shipped with preinstalled malware designed to generate fraudulent ad revenue.
The crypto wallet maker verified that tampered units distributed by a Southeast Asian reseller contained unauthorized implants that drained user funds.
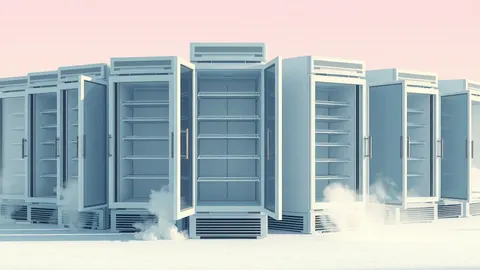
Attackers remotely triggered automatic defrost cycles in hundreds of French stores, affecting major chains and causing significant food waste and financial losses.
A weekly bulletin from Check Point Research outlines major data exposures in Denmark and Japan, alongside new exploits in enterprise software.
Attackers use live WebSockets to bypass MFA by relaying authentication steps in real time to operators.
Hackers reportedly raised temperatures in French retail refrigeration units, spoiling food stocks and impacting operations in the Netherlands.
Cybercriminals reportedly altered cooling settings at major French chains, causing units to heat up and forcing the disposal of perishable goods.
Canonical confirmed on October 8 that its primary web properties faced a sustained distributed denial-of-service attack, marking the second such incident this year.
Operational Technology ISAC and Singapore university partner on threat intel and research to strengthen critical infrastructure resilience.
A dual citizen admitted to running a scheme that recruited thousands of Americans to launder millions for cybercriminals.
Security experts found that specific Cyrillic characters bypass Chromium's display rules, enabling fake domains to appear as trusted brands without Punycode warnings.
A GPU technician revealed a high-effort scam involving a fake graphics card with dummy silicon and swapped memory chips sold for $350.
Attackers embed concealed commands in emails to manipulate AI inbox summarizers into generating fraudulent to-do items for recipients.
Bitdefender discovered the Midnight Mimosa campaign, which embeds persistent malware in the firmware of low-cost Android devices sold online.
Federal agents expand crackdown on extortion crew while Anthropic's Mythos model uncovers a second exploited vulnerability that humans likely missed.
Researchers identify a spear-phishing operation using AI-assisted event invitations to steal credentials from Taiwanese research affiliates by intercepting Google authentication sessions.
A financial document lure delivered via WhatsApp deploys malware that hijacks the Windows Task Scheduler to execute payloads with LocalSystem privileges, bypassing standard security checks.
Brad Smith told ITV that artificial intelligence faces fewer safety regulations than dairy products, hoping the UK will lead on policy.