Dutch and Israeli researchers find thousands of exposed wind and solar systems in Europe
A joint study by Modat and NCSC-NL reveals over 8,500 internet-facing renewable energy systems across 35 countries that lack proper access controls.
Key points
- Researchers identified 8,547 exposed systems at wind farms and solar parks in and around the EU.
- The systems range from login screens to turbine control pages with remote stop capabilities.
- Operators in Spain, Greece, Italy, and Germany account for the majority of confirmed exposures.
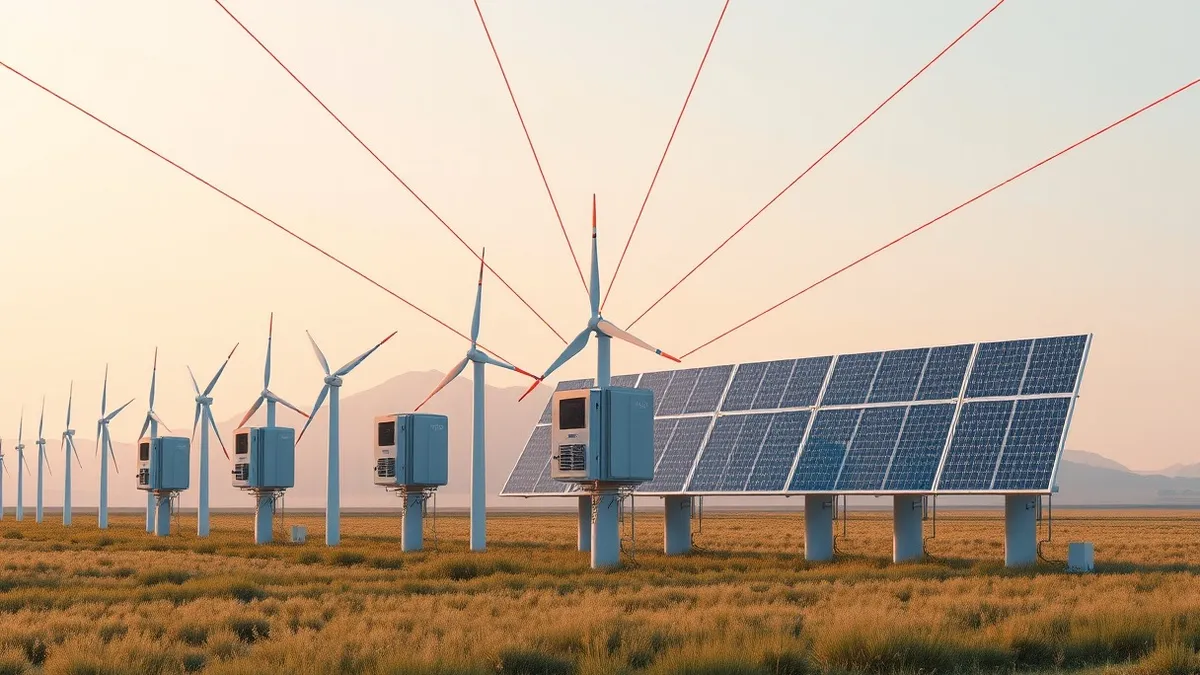
Researchers from Modat and the Dutch National Cyber Security Centre (NCSC-NL) have identified more than 8,500 internet-facing systems at wind farms and solar parks across Europe that should not be accessible from the public internet, according to Help Net Security. The joint investigation uncovered these critical infrastructure components in 35 countries within and surrounding the European Union, highlighting a widespread failure in network segmentation for renewable energy assets.
The exposed systems present significant operational risks, ranging from simple login screens to fully functional turbine control interfaces. According to the report, some of these control pages offer a "Stop" button that is accessible to anyone with a web browser, potentially allowing unauthorized users to halt energy generation remotely. The researchers noted that the confirmed number of 8,547 systems is likely a conservative estimate, as the actual figure is probably higher due to the limitations of automated scanning and the dynamic nature of internet-connected devices.
Geographic Distribution and Scope
The study found that operators in Spain, Greece, Italy, and Germany account for the largest share of the confirmed exposed systems. While the research focused on the European region, the findings indicate a systemic issue in how renewable energy infrastructure is connected to external networks. The systems identified are part of wind and solar parks, which are increasingly critical to the region's energy grid. The presence of these internet-facing endpoints suggests that many operators have not implemented adequate perimeter defenses or have misconfigured their network architecture, leaving critical control functions vulnerable to external access.
Operational Risks and Exposure
The nature of the exposure varies, but the potential impact remains severe. The discovery of login screens indicates that authentication mechanisms are reachable from the internet, which could facilitate brute-force attacks or credential stuffing. More concerning are the turbine control pages that allow direct interaction with the physical equipment. The ability for an external actor to press a stop button on a turbine control page demonstrates a direct link between internet exposure and physical operational disruption. This lack of isolation between the corporate or public internet and the operational technology (OT) network violates standard security practices for critical infrastructure.
What should you do?
Organizations managing renewable energy infrastructure should immediately audit their network perimeter to identify any unexpected internet-facing assets. Security teams should verify that all operational technology networks are properly segmented from corporate and public networks. Operators should review firewall rules and access control lists to ensure that only authorized management interfaces are accessible, and preferably only via secure, authenticated channels such as VPNs. Continuous monitoring for new internet-exposed assets is essential to detect misconfigurations before they can be exploited.
What to do and how to stay safe: Modat
- Conduct a comprehensive scan of your external network perimeter to identify any internet-facing devices associated with operational technology.
- Verify that all control systems and management interfaces are strictly segmented from public networks and not directly routable from the internet.
- Review and restrict firewall rules to ensure that only necessary, authenticated administrative access is permitted, ideally through a secure jump host or VPN.
- Monitor for unauthorized changes to network configurations that might inadvertently expose critical infrastructure components to the public internet.
General security guidance from the Threat Times newsroom. It is not confirmed advice from the organisations named in this story.
Frequently asked questions
How many systems were found to be exposed in this study?
Researchers identified 8,547 internet-facing systems at wind farms and solar parks across 35 countries.
Which countries had the most exposed systems?
Operators in Spain, Greece, Italy, and Germany accounted for the majority of the confirmed exposed systems.
What kind of access do these exposed systems provide?
The systems range from login screens to turbine control pages that allow remote stopping of equipment via a web browser.