AI
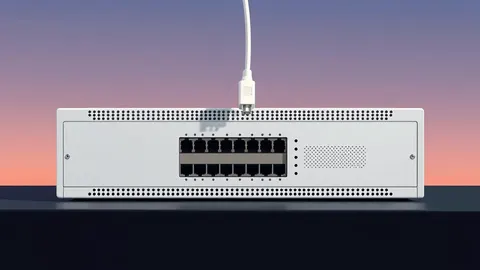
Cisco ships Silicon One G300, unveils G302 chip for AI data centers
Cisco announced volume shipments of its 102.4-Tbps silicon and revealed a new top-of-rack switch to address AI networking bottlenecks.
Everything Threat Times has reported about Cisco: 14 stories, newest first. Part of our Vulnerabilities coverage.
Cisco announced volume shipments of its 102.4-Tbps silicon and revealed a new top-of-rack switch to address AI networking bottlenecks.
Rising latency and bandwidth constraints are hindering AI adoption as organizations struggle to move data at machine speed.
ThousandEyes reports a sharp decline in global and US network disruptions for the week of September 28 through October 4, with cloud outages falling significantly.
Major cloud providers are linking datacenters over long distances to coordinate thousands of GPUs for large-scale model training.
Cisco Talos launches its inaugural newsletter, offering practitioners insights into maintaining business continuity when perfect security patches are unavailable.
Cisco has released security advisories for five critical flaws in its NX-OS data center operating system that could allow attackers to execute arbitrary code with root privileges on Nexus switches.
Cisco has issued fixes for twelve critical security flaws that could allow attackers to execute code remotely or escalate privileges on affected systems.
Cisco has issued software updates addressing multiple critical vulnerabilities across its License On-Prem, NX-OS, and Meraki platforms following internal security reviews.
Cisco releases software updates for Application Policy Infrastructure Controller addressing command injection and file access vulnerabilities.
Cisco has released updates for critical remote code execution vulnerabilities in Nexus 3000 and 9000 series switches affecting MPLS and NGOAM features.
Cisco has issued a high-severity advisory for CVE-2026-20362, an unauthenticated server-side request forgery flaw in Cisco Finesse that allows remote attackers to access sensitive service information.
Cisco has released software updates for two vulnerabilities in NX-OS, including a Python sandbox escape and a remote denial-of-service flaw.
Cisco has released software updates to fix a critical, unauthenticated remote code execution flaw in NX-OS NX-API that allows root access.
Evidence of real-world attacks puts CVE-2026-76504 on CISA's KEV list, with a remediation deadline of October 3, 2026.