
Cyber Attacks
AWS publishes guide for ML-DSA quantum-resistant signing in software supply chains
Amazon Web Services released a two-part series detailing how to build and enforce post-quantum signing pipelines using NIST-standardized algorithms.
Everything Threat Times has reported about AWS: 50 stories, newest first. Part of our Vulnerabilities coverage.
Amazon Web Services released a two-part series detailing how to build and enforce post-quantum signing pipelines using NIST-standardized algorithms.

The open-source tool uses policy checks and OS isolation to prevent coding agents from executing destructive commands or leaking credentials.

Reports indicate Amazon is negotiating a potential $7 billion acquisition of AI infrastructure developer Decart, aiming to bolster its cloud computing capabilities.
Palo Alto Networks and Zenity Labs report that AWS AgentCore default settings allow credential exfiltration via prompt injection, illustrating broader AI agent risks.
Russian tech giant Yandex warns that its ru-central1-b cloud zone may not be restorable in the near future after a drone strike halted operations.
New tools from Cloudflare and AWS aim to handle routine AI agent decisions locally, potentially lowering costs but increasing architectural complexity.
Major cloud providers are linking datacenters over long distances to coordinate thousands of GPUs for large-scale model training.
New findings indicate a single prompt could compromise Amazon Bedrock AgentCore, exposing credentials and private data within the same account and region.
A new attack chain dubbed AgentCorruption allows attackers to hijack AI agents via a single prompt, leading to credential theft and lateral movement within AWS accounts.
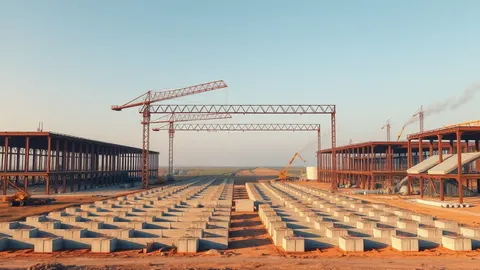
Amazon Web Services is constructing a massive facility in Homer City, backed by 4.5GW of natural gas generation and creating up to 2,000 jobs.
Analysis reveals that AWS AgentCore’s security model is undermined by metadata token transmission, weak virtual machine isolation, and overly expansive permissions.
Amazon Web Services has issued a security bulletin regarding a stack buffer overflow vulnerability in its C Event Stream Streaming Decoder.
Amazon Web Services released security bulletins for CVE-2026-6911 and CVE-2026-6912, addressing issues in its Ops Wheel service.
AWS has published a security bulletin detailing CVE-2026-5747, an out-of-bounds write flaw in the Firecracker microvm manager’s virtio-pci transport component.
A new advisory from Amazon Web Services details a high-severity vulnerability allowing arbitrary code execution through a sandbox escape.
Amazon Web Services disclosed a command injection flaw in the ECS Agent that affects users with FSx Windows File Server volumes.
A vulnerability in the Amazon Redshift JDBC driver allows remote code execution through unsafe class loading, posing risks to connected applications.
A new security bulletin highlights an authorization bypass flaw in the Kiro CLI, allowing unauthorized tool execution via piped standard input.
Amazon Web Services has published advisory details for two new vulnerabilities, identified as CVE-2026-11400 and CVE-2026-11401, requiring immediate attention.
AWS issued a security bulletin for two CVEs in WAF that could let attackers bypass inspection rules via HTTP/2 multi-frame requests.
A flaw in the AWS Encryption SDK for Python allows attackers to bypass key commitment policies by exploiting a shared key cache mechanism.
Amazon Web Services released a security bulletin for CVE-2026-6437, addressing a vulnerability in the EFS CSI Driver that could allow unauthorized file system access.
Amazon Web Services has published a security bulletin addressing issues within its Research and Engineering Studio service.
Amazon Web Services has released a security bulletin addressing issues within the Amazon Athena ODBC Driver, urging users to review their configurations.